Cybersecurity
Penetration testing, security reviews and hardening that find the gaps before attackers do, with clear fixes your team can act on.
What you get
- Web application penetration testing based on the OWASP Top 10
- Security review of code, authentication and infrastructure configuration
- A prioritised report with clear, practical fixes
- Help implementing the fixes and re-testing afterwards
A good fit for
- Products about to launch or handle sensitive data
- Teams preparing for a client security questionnaire or audit
- Businesses that want to know where they stand after an incident
How it works
- 1
Free intro call
A 30-minute call to understand your goals, constraints and timeline.
- 2
Scope & plan
A clear written scope with milestones, risks and an estimate, before any work starts.
- 3
Build & review
Work in short iterations with regular updates, so you see progress and steer early.
- 4
Launch & support
A careful release, a handover you can follow, and support after launch.
Related work

Decoding OAuth Flow
A clean demo of the OAuth 2.0 flow — secure authentication, designed and explained the right way.
Read the case study →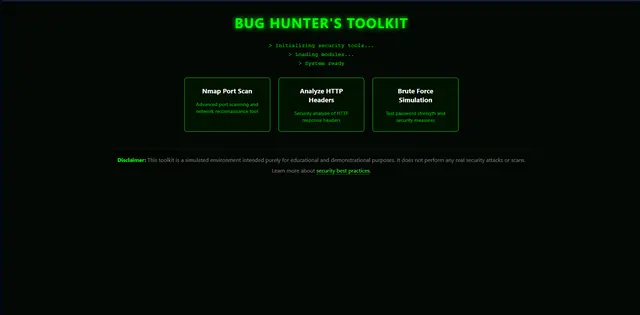
Simulating the Hunt
A controlled environment demonstrating penetration-testing logic and ethical, responsible security practice.
Read the case study →
Inside the Half Half Man Portfolio
A secure, full-stack site in React, Tailwind, and Sanity — proof of clean architecture, speed, and multilingual reach.
Read the case study →
Questions
Testing of authentication, access control, input handling, session management and configuration, following the OWASP guidelines, plus a review of how secrets and data are handled.
Testing is agreed in advance and scoped to avoid disruption. Where possible it runs against a staging environment.
Both. You get a prioritised report, and we can implement the fixes or work alongside your team.
Have a project in mind?
Tell Half Half Man what you are building. A free 30-minute call is enough to scope it, spot the risks and agree on next steps.
Book a free 30-min call